發表文章

腳本 acarsd-info 說明

Acars Devoder port 2202 官方網站:  1.    https://nmap.org/nsedoc/scripts/acarsd-info.html  2.    http://www.acarsd.org/server_howto.html  3.    https://play.google.com/store/apps/details?id=com.blackcatsystems.acars&hl=zh_TW ==================================== 內容: local comm = require "comm" local nmap = require "nmap" local shortport = require "shortport" local stdnse = require "stdnse" local string = require "string" local table = require "table" description = [[ Retrieves information from a listening acarsd daemon. Acarsd decodes ACARS (Aircraft Communication Addressing and Reporting System) data in real time.  The information retrieved by this script includes the daemon version, API version, administrator e-mail address and listening frequency. For more information about acarsd, see: * http://www.acarsd.org/ ]] --- -- @usage -- nmap --script acarsd-info --script-args "acarsd-info.timeout...

查看服務(port)所用的軟體

圖片
一台伺服器有時會開很多個服務, 例如: HTTP(80), FTP(21)等等 查閱出這些服務(port)所用的軟體 可以幫助再進一步檢查 是否 有漏洞 指令:  nmap -sV    IP address 若是要 加強查詢 伺服器版本, 可加上-A 用來針對目標物(IP位址或 伺服器網域名稱)之內安裝服務  詳細版本訊息 說明:   nmap  -sV --version-trace  IP位址

腳本編輯器 Notepad++

圖片
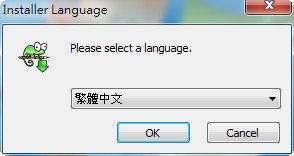
其實有專屬NSE的腳本編輯器~ Halcyon-master 但是因為不能win下安裝, 所以不推薦 考量很多因素, 我推薦使用 Notepad++這套 官方網址:  https://notepad-plus-plus.org/ 免安裝版:   http://www.azofreeware.com/2006/10/notepad-35.html   ( 阿榮福利味 ) 以下是到官網去下載安裝版

腳本 命名的 特性

腳本 命名的 特性 auth: 檢測判定類型的脚本 broadcast: 查看port 狀況,如dhcp/dns/sqlserver等服务 brute: 暴力破解可能的漏洞 default: 使用-sC或-A 去掃描基本特性 discovery: 查詢網路上的訊息 dos: 使用DOS攻擊 exploit: 利用已知的漏洞入侵系统 external: 利用第三方的資料庫查詢, 例如透過whois解析 fuzzer: 模糊方式去偵測出潛在漏洞, 是入侵性 intrusive 的脚本 malware: 偵測是否感染了病毒、後門等訊息 safe: 與intrusive相反,比較是安全性脚本 version: 針對作業系統+iis+sql等版本功能的脚本 vuln: 檢查是否有漏洞(Vulnerability),例如: XP否有MS08_067補救 官方查詢: https://nmap.org/nsedoc/scripts/mysql-info.html

-Pn 用法

隱藏或說刁鑽的目標(電腦\防火牆\設備) 並不回應ping 也關閉常用port80等等.... 若要揪出來, 就可能用-Pn 從存在的port 1732, 8000去推斷及測試 ========================= 例如:  nmap -Pn 180.177.99.88 Starting Nmap 7.12 ( https://nmap.org ) at 2016-05-30 06:27 ¥x¥_?D·CRE?! Nmap scan report for 180-177-99-88.dynamic.kbronet.com.tw (180.177.99.88) Host is up (0.074s latency). Not shown: 998 filtered ports PORT     STATE SERVICE 1723/tcp open  pptp 8000/tcp open  http-alt Nmap done: 1 IP address (1 host up) scanned in 17.18 seconds =========================

ICMP ping 方式 PE PP PM

圖片
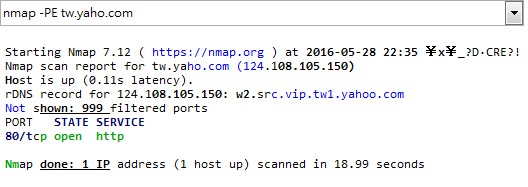
nmap 掃描主機方式很多 這次介紹ICMP (Internet Contorl Message Protocol)方式 -PE : 發送ICMP Echo封包  去偵測主機是否活著~ 發送type8 , 回來是type0 -PP: 使用 ICMP time stamp -PM: 隱蔽地址 的ICMP ping 針對tw.yahoo.com, 發現答案的不同 接著要偵測.....設備是哪一種, 還有哪些回應? 哈哈 ICMP說明: http://www.pcnet.idv.tw/pcnet/network/network_ip_icmp.htm

TCP SYN 與 ACK ping偵測

圖片
一般nmap 的ping 內定是ICMP echo方式偵測 但如被防火牆擋住, 那回應就是 host down 所以 建議偵測  要多加TCP SYN 指令: nmap -PS  IP address  (使用 TCP SYN) 指令: nmap -PA  IP address  (使用 TCP ACK)